
Advantech routers are highly versatile and support a wide range of applications. This chapter describes several common deployment scenarios step by step. Each use case explains what it solves, shows the network topology, lists the prerequisites, and guides you through the configuration and its verification.
The configuration examples provided in this chapter are based on IPv4 networks. Each use case assumes that you have completed the Initial Setup and can log in to the router's web interface.
Tips
Use cases that rely on a cellular connection apply only to router models with a cellular module.
Access to the Internet from LAN
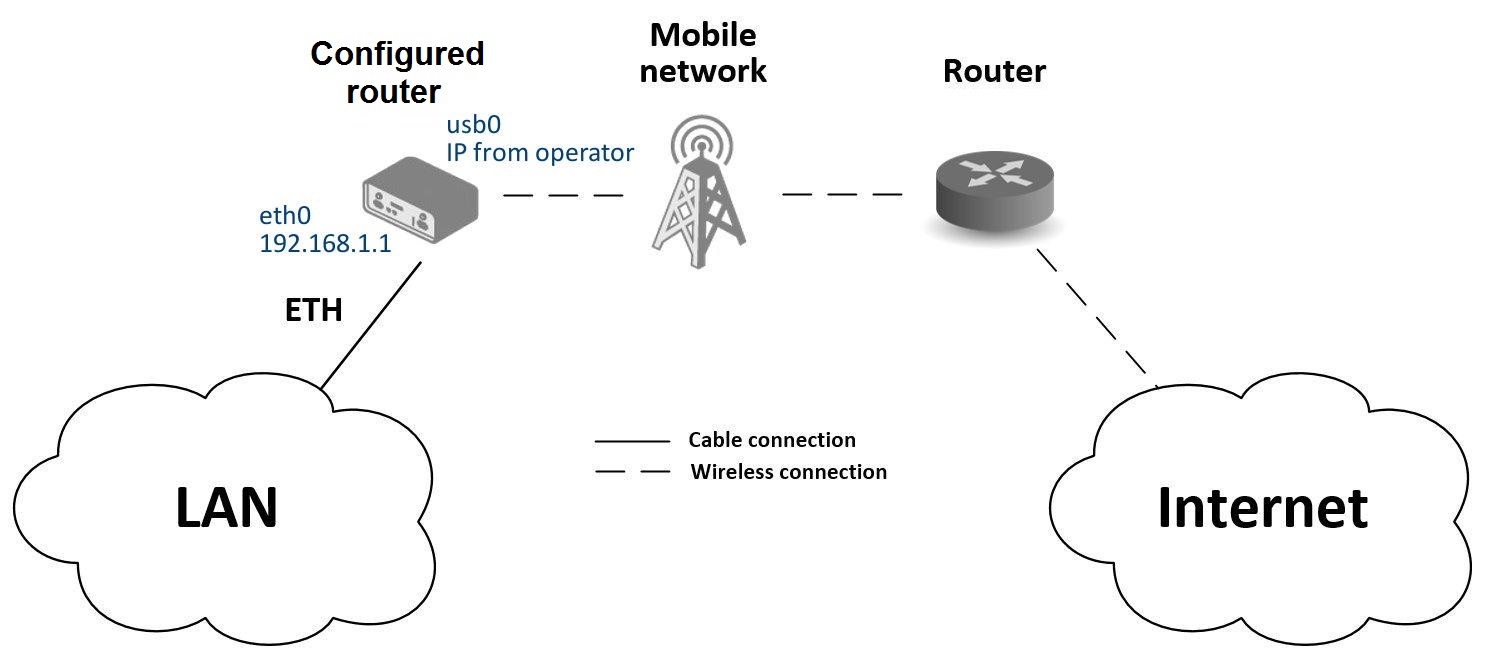
What it solves: Devices on a local area network (LAN) need Internet access at a site without a wired Internet connection. The router provides Internet access to the entire LAN through its cellular connection.
Prerequisites
- An active SIM card with a data plan from a mobile network operator, inserted into the SIM1 slot. See SIM Card Slots.
- Antennas attached to all cellular antenna connectors of the router. The connector names depend on the model; see Antenna Connections. If your router includes Wi-Fi or GNSS capabilities, attach their antennas as well.
- A computer or a local network switch connected to the router's ETH0 port.
- The router connected to the power supply.
Configuration
While factory settings are often sufficient, you can review or modify the configuration in the router's web interface via the Configuration section.
Ethernet Configuration
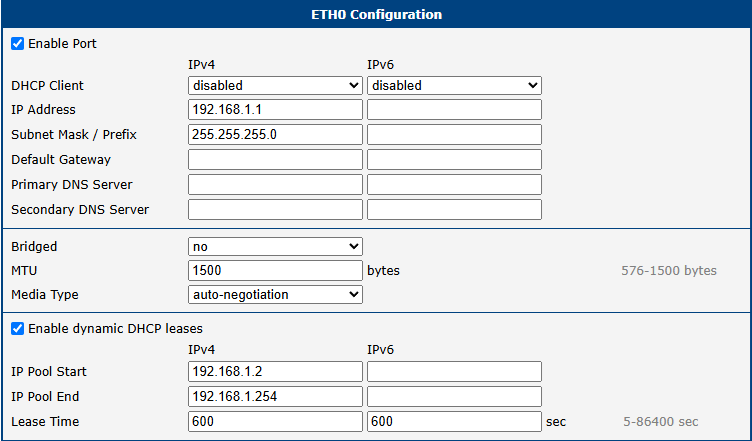
Navigate to Configuration → Ethernet. The LAN interface (ETH0) is pre-configured with a static IP address of 192.168.1.1. The DHCP server is also enabled by default, automatically assigning IP addresses to connected devices (the first device receives 192.168.1.2, and so on). No changes are needed for this use case.
Mobile WAN Configuration
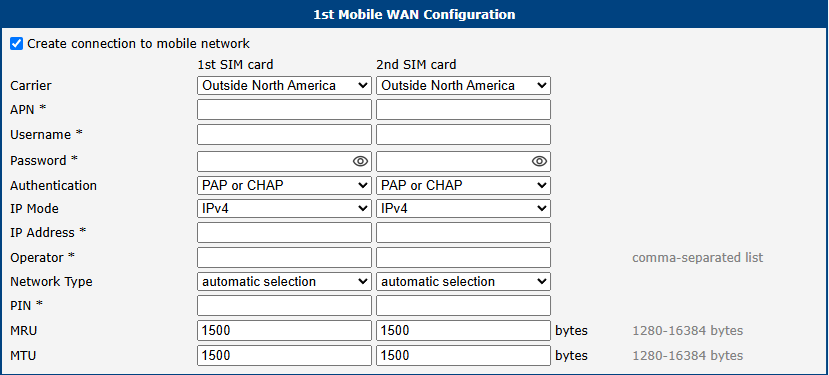
Navigate to Configuration → Mobile WAN. Ensure that the Create connection to mobile network option is enabled (the default setting). For most public SIM cards, you do not need to fill in the APN, username, or password.
Verification
After powering on, wait for the router to register on the mobile network. The LED indicators show the state of the cellular connection; see LED Indicators.
Navigate to Status → Mobile WAN. This page displays key details about the connection, including the operator, signal strength, and a Connection successfully established message. You can also inspect Status → Network to see the new mobile interface (rmnet0) and the IP address assigned by the operator. Once confirmed, all devices on the LAN have Internet access.
Backup Access to the Internet from LAN
What it solves: A single Internet connection is a single point of failure. With the Backup Routes feature, the router uses several Internet sources with defined priorities and automatically switches to a lower-priority connection if a higher-priority one fails, ensuring continuous Internet access for the LAN. Depending on the router model, the sources can include a wired Ethernet connection, a PPPoE connection, a Wi-Fi connection, and the cellular connection.
A typical scenario is LTE failover, where the cellular (Mobile WAN) connection automatically backs up the primary wired or Wi-Fi WAN connection.
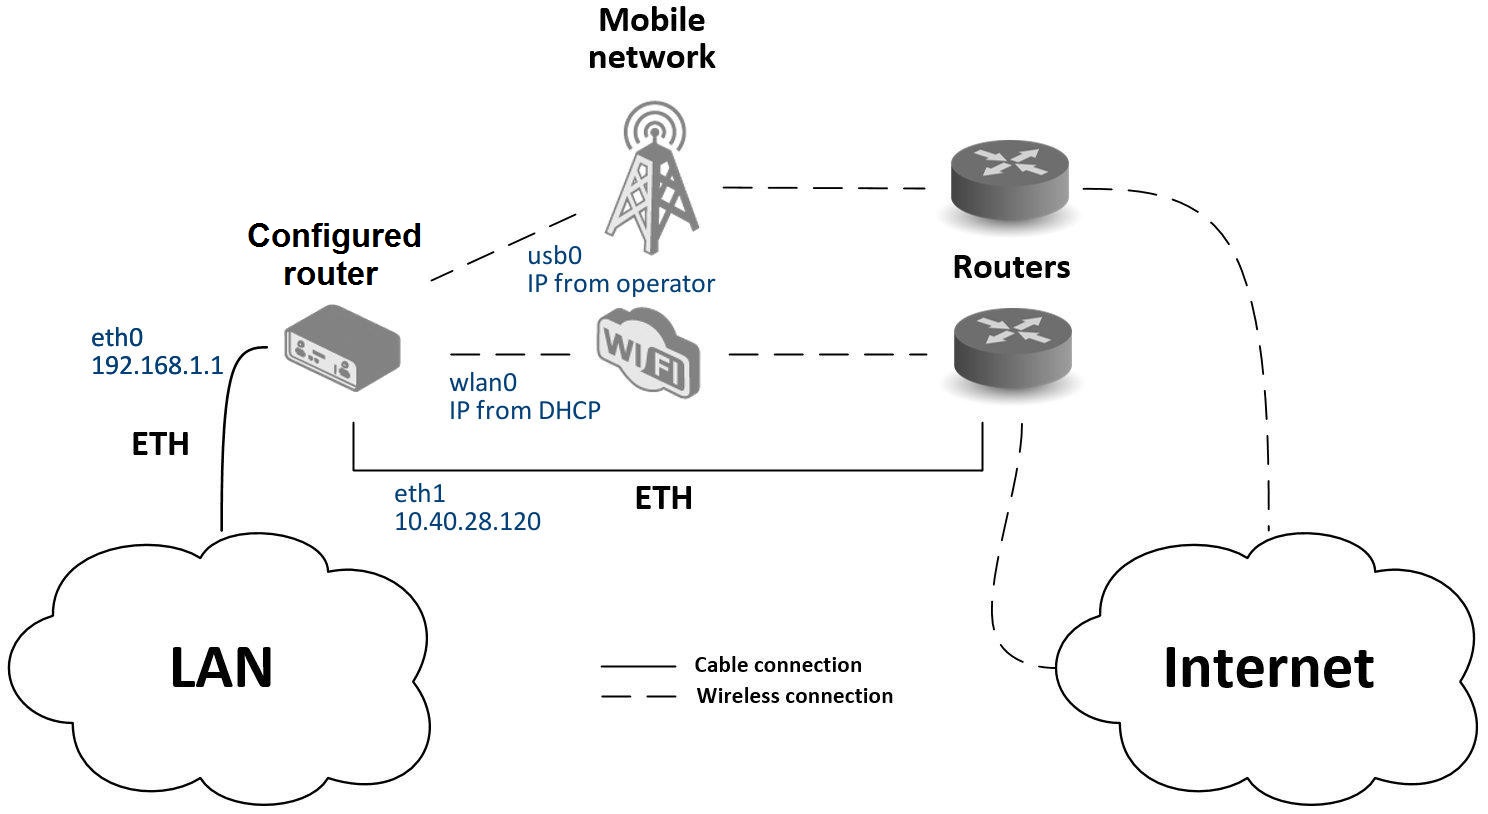
In this example, the wired connection on the ETH1 port is the primary Internet source, Wi-Fi is the first backup, and the cellular connection is the final backup.
Prerequisites
- An Internet connection on the
ETH1port, with the static IP address, subnet mask, default gateway, and DNS server provided by your Internet Service Provider. - Access to a Wi-Fi network that provides an Internet connection (for models with Wi-Fi).
- An active SIM card inserted into the SIM1 slot and the cellular antennas attached. See SIM Card Slots and Antenna Connections.
- The LAN interface (
ETH0) at its default settings.
Configuration
Configure each interface that will serve as an Internet source, and then set their priorities.
Ethernet WAN Configuration
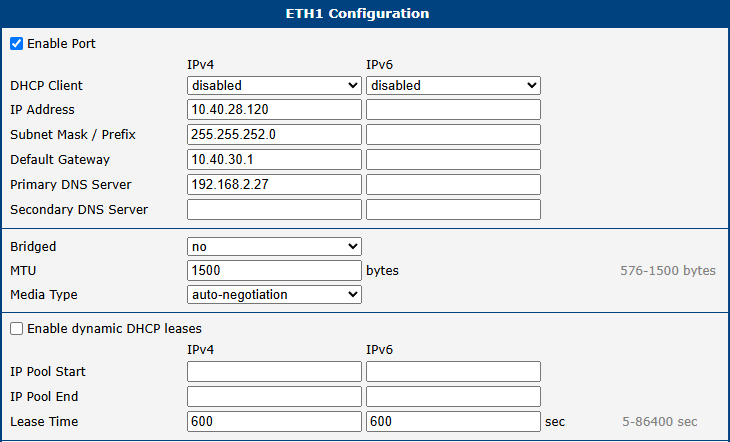
The ETH1 port is used as the primary wired WAN connection.
- Navigate to Configuration → Ethernet → ETH1.
- Configure the interface with a static IP address, subnet mask, default gateway, and DNS server provided by your Internet Service Provider.
- Click Apply to save the changes.
Wi-Fi WAN Configuration
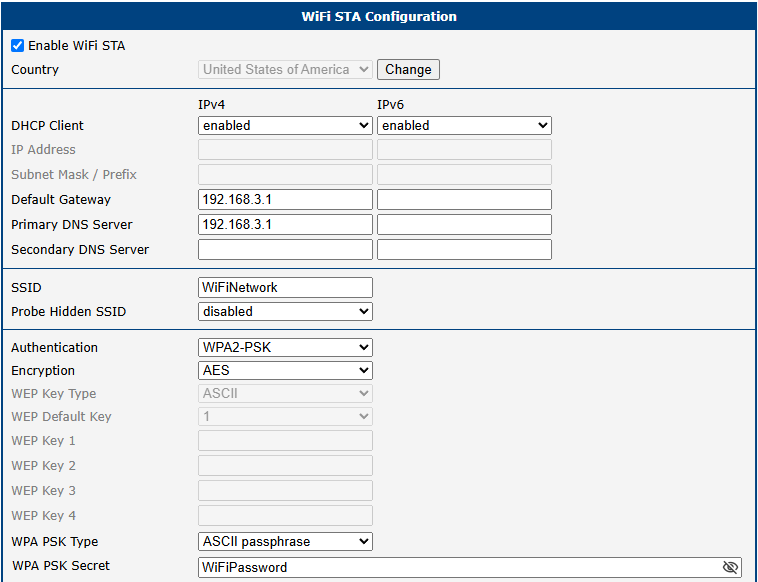
To use Wi-Fi as a backup connection, configure the router as a client (Station) to another Wi-Fi network.
- Navigate to Configuration → WiFi → Station.
- Check Enable WiFi STA.
- If the Wi-Fi network provides settings automatically, enable the DHCP client. Otherwise, manually enter the default gateway and DNS server addresses.
- Enter the network's SSID and select the appropriate Authentication, Encryption, and WPA PSK Type.
- Enter the Wi-Fi password and click Apply.
Mobile WAN Configuration
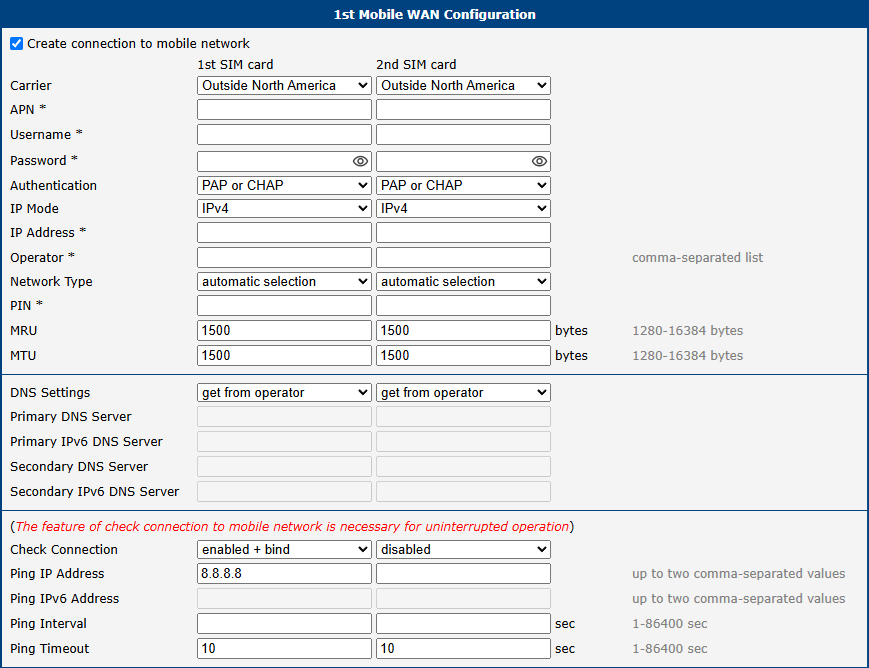
The cellular connection serves as the final backup. To integrate it into the backup system:
- Navigate to Configuration → Mobile WAN.
- Set the Check connection option to enabled + bind.
- Enter a reliable IP address to ping (e.g., your operator's DNS server) and set the check interval.
Backup Routes Configuration
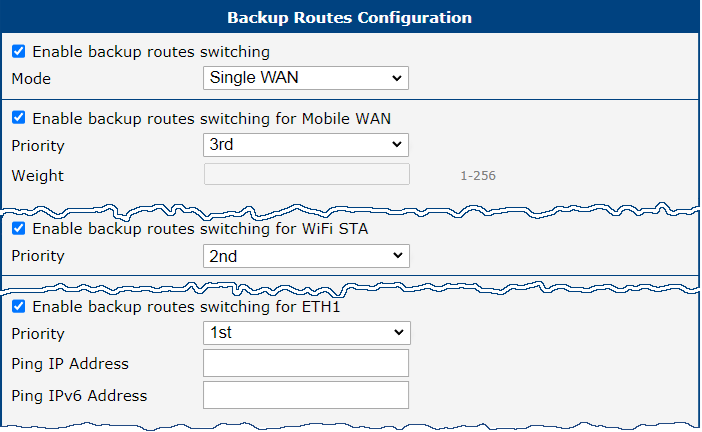
After configuring the interfaces, set their priority in Configuration → Backup Routes.
- Set the priority for each WAN interface:
- 1 (Highest):
eth1(Wired Ethernet) - 2 (Medium):
wlan0(Wi-Fi) - 3 (Lowest):
rmnet0(Cellular)
- 1 (Highest):
- Check Enable backup routes switching for each route.
- Click Apply to save the configuration.
Verification
To check the Wi-Fi connection, navigate to Status → WiFi. A successful connection shows wpa_state=COMPLETED.
Monitor all network interfaces under Status → Network. The route table at the bottom of the page shows which interface is currently active as the default route. If eth1 fails, the default route switches to wlan0. If wlan0 also fails, it switches to rmnet0.
Secure Network Interconnection with VPN
What it solves: Two or more separate LANs need to communicate securely over an untrusted public network, such as the Internet. A Virtual Private Network (VPN) creates an encrypted tunnel between the routers, so the LANs communicate as if they were a single private network. This ensures both the confidentiality and integrity of the exchanged data.
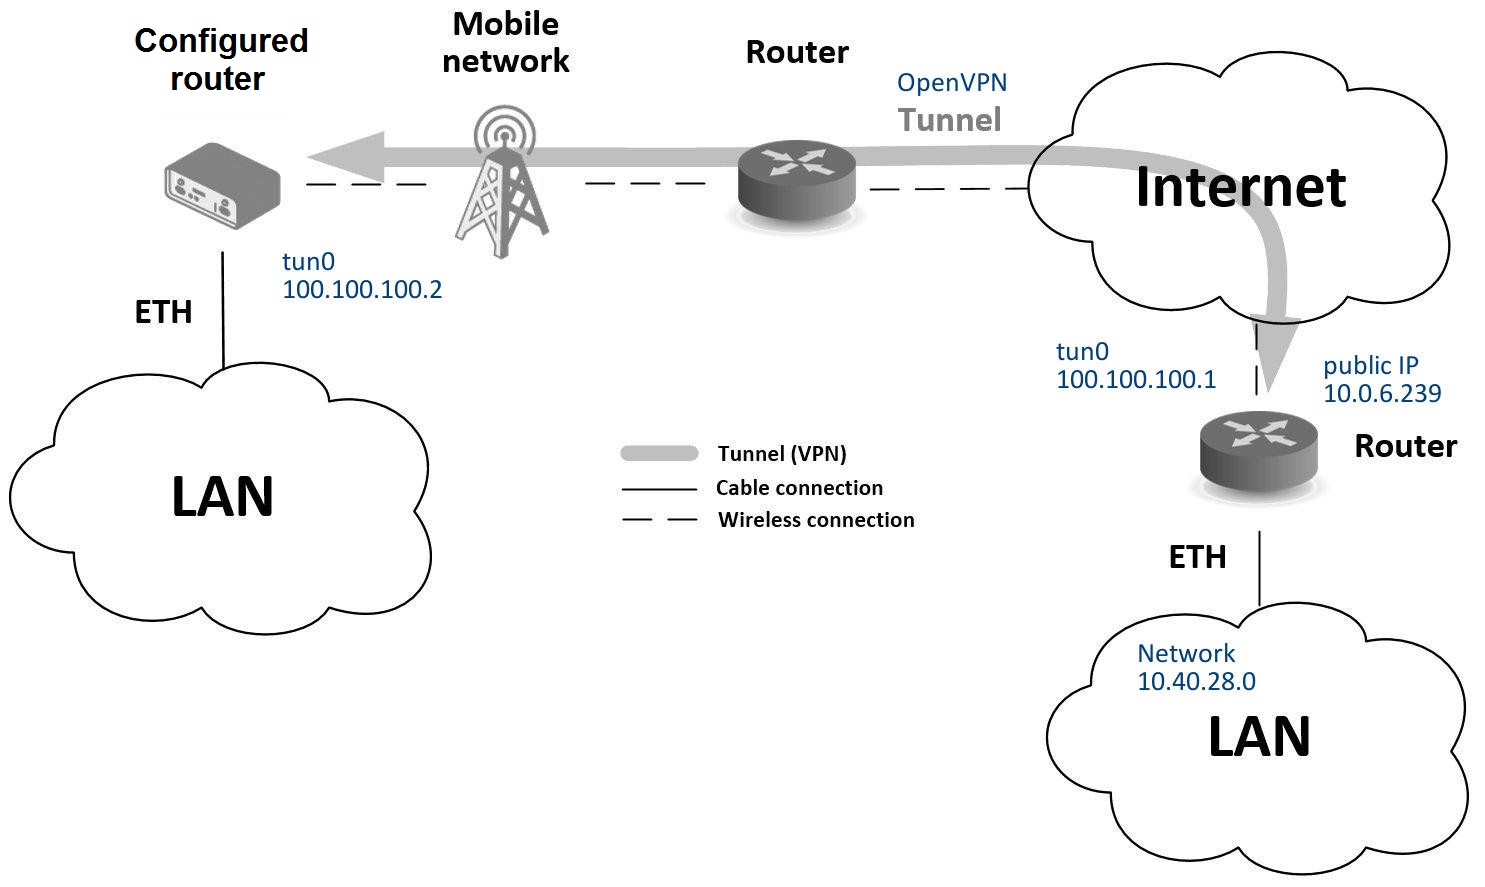
Advantech routers support several VPN protocols, including:
- OpenVPN: A highly flexible and secure SSL/TLS-based VPN.
- IPsec: A standards-based framework for securing IP communications.
The router also supports non-encrypted tunneling protocols such as GRE, PPTP, and L2TP, which can be combined with IPsec to create secure VPNs.
This example demonstrates how to establish an OpenVPN tunnel between two routers using a pre-shared secret key for authentication.
Prerequisites
- A stable Internet connection on both routers. In this example, the router connects through the cellular network: insert an active SIM card, attach the antenna, and make sure that the mobile connection is established, as described in Access to the Internet from LAN.
- The public IP address of the remote router.
- The tunnel settings of the remote router (protocol and port) and its pre-shared secret key.
Configuration
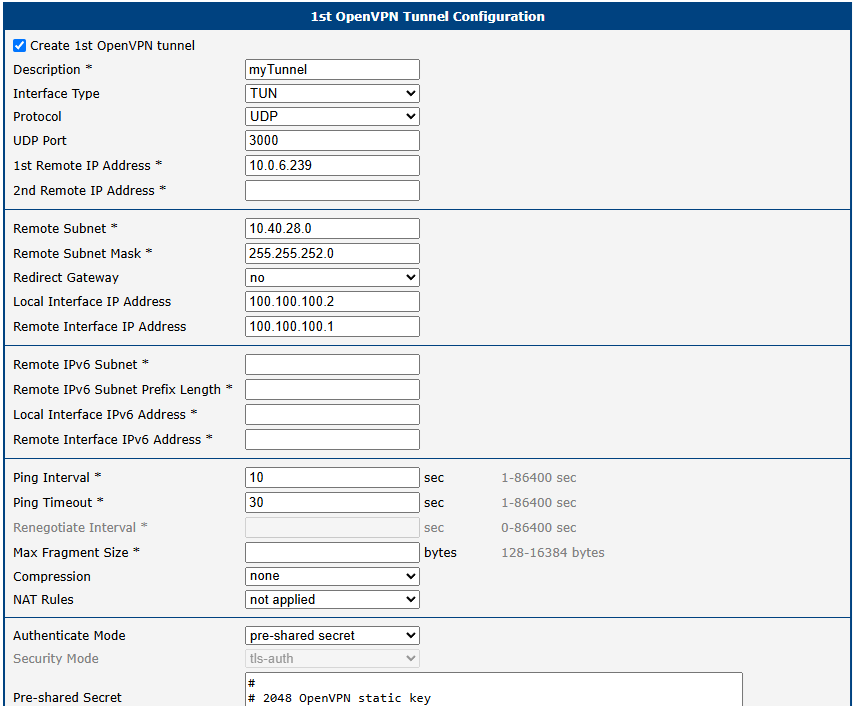
- Navigate to Configuration → OpenVPN.
- Enable one of the available tunnels by checking Create 1st OpenVPN tunnel.
- Set the Protocol and UDP/TCP port to match the settings of the remote router.
- In the 1st Remote IP Address field, enter the public IP address of the remote router.
- In the Authenticate Mode dropdown, select pre-shared secret.
- Paste the pre-shared secret key into the Pre-shared Secret field.
- Define the virtual IP addresses for the tunnel endpoints in Local Interface IP Address and Remote Interface IP Address. These must form a mini-subnet for the tunnel (e.g.,
10.8.0.1and10.8.0.2). - Click Apply to save the configuration.
Verification
Confirm that the VPN tunnel is active:
- Network Status: Navigate to Status → Network. A new virtual interface
tun0should be listed with the IP address you configured. - System Log: Navigate to Status → System Log. Look for an
Initialization Sequence Completedentry, confirming the OpenVPN tunnel is established.
Once the tunnel is active, you can verify it by pinging the remote tunnel endpoint's IP address from the router's command-line interface via SSH.
Serial Gateway
What it solves: Serial devices, such as PLCs, meters, or sensors, have no network interface of their own. The Serial Gateway feature encapsulates serial data into IP packets and creates a virtual serial port across the Internet, so a central SCADA system or a remote PC can collect data from or control the serial equipment.
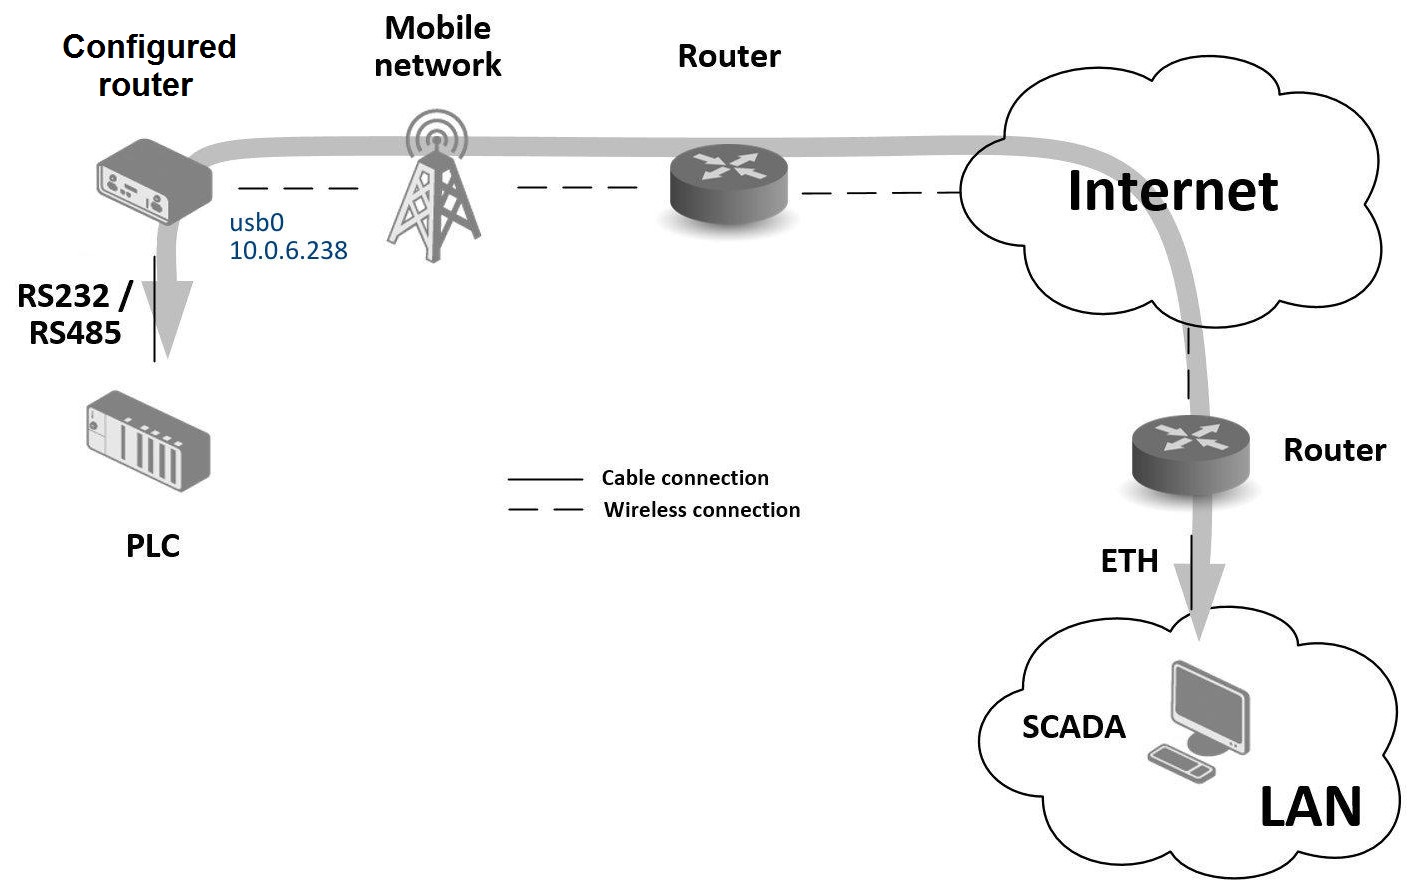
In this example, the router's RS-232 port is connected to a PLC, and the router is configured as a TCP server. A remote PC (SCADA) connects as a TCP client to communicate with the PLC.
Prerequisites
- A stable Internet connection. In this example, the router uses its cellular connection: insert an active SIM card into the SIM1 slot and attach the cellular antennas. The router automatically connects to the mobile network. For more details, see Mobile WAN.
- The public IP address assigned to the router by the mobile operator. The remote client uses it to connect to the serial gateway.
- The PLC connected to the router's RS-232 port, with known serial communication parameters (baud rate, data bits, parity, and stop bits).
Configuration
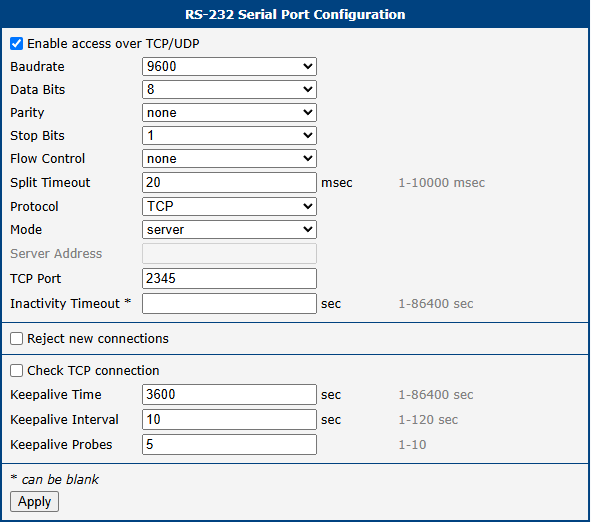
- Navigate to Configuration → Peripheral Ports → RS-232.
- Check Enable access over TCP/UDP.
- Set Protocol to
TCP. - Set Mode to
server. The router will listen for incoming connections. - In the TCP Port field, enter the port number on which the router will listen (e.g.,
2345). - Configure the serial communication parameters (Baud Rate, Data Bits, Parity, etc.) to match the connected serial device.
- Click Apply to save the configuration.
Verification
The remote PC (SCADA) can establish a TCP connection to the router's public IP address (e.g., 10.0.6.238) on the configured port (e.g., 2345). All data sent over this TCP session is forwarded to the PLC via the serial port, and vice versa.
Monitor the connection status in Status → System Log. When the remote client connects successfully, a TCP connection established message appears in the log.